webfilteringdatabase.com
Home Find Your Solution
Features
Domain Categorization API Real-Time Classification 58 Filtering Categories Offline Database (120M) SaaS App Hostnames Managed DNS Filter ML Classification Content Classification
Industries
K-12 Schools Corporate Healthcare Government ISPs
Tools
Domain Lookup Bulk Categorization Category Explorer
Resources
Pricing API Documentation Login / Sign Up
Knowledge Base

Content Risk Intelligence Integration

Feed domain category and content-risk intelligence into your SIEM, SOAR, secure web gateway, DNS, and proxy stacks. Turn 120 million classified domains and 58 categories into real-time enrichment and category-based risk scoring across your entire security architecture.

120M+Classified Domains
58Content Categories
<10msLookup Latency
HourlyDelta Updates

What Content Risk Intelligence Adds to Your Stack

Every security stack already sees domains — in firewall logs, proxy records, DNS queries, and email URLs — but a raw domain string carries almost no meaning on its own.

Content risk intelligence is the layer that turns that string into a decision:
  • what category the domain belongs to
  • how risky that category is in your context
  • which policy or playbook should fire as a result
The Web Filtering Database provides this layer as a single, consistent source of truth. Instead of maintaining separate blocklists in every tool, you enrich all of them from one intelligence source.
Every domain in a corpus of more than 120 million is evaluated against 58 content categories with a multi-label model, so one lookup tells your stack whether a destination is business software, streaming, file-sharing, phishing, or one of dozens of other categories — and whether it carries elevated content risk.
The value of that consistency compounds as it spreads across the architecture. When your firewall, your SIEM, your secure web gateway, and your DNS resolver all reason about the same categories, your policies become coherent, your correlation rules become simpler, and an analyst investigating an alert sees the same category context everywhere they look.
One intelligence layer, every enforcement point

One Source, Every Tool

Enrich firewall, SIEM, SWG, DNS, and proxy from a single category intelligence feed.

Real-Time Enrichment

Sub-10ms API lookups add category and risk context inline without slowing traffic.

Category Risk Scoring

Map 58 categories to your own risk tiers for consistent, tunable policy decisions.

One source behind every alert

Stop keeping a separate domain list in each security tool

Your gateway, SIEM and resolver all see hostnames, and each one deserves the same answer about them. We license the category records so every tool enriches from a single source.

  • Pull the data as CSV or JSON, query the real-time API, or run the offline database.
  • Turn the categories into your own risk tiers and playbook triggers.
  • Rely on daily additions so a brand new hostname is rarely a blank.
Category records used to enrich hostnames in security tools
~300,000
domains categorized fresh each day for enrichment
120M+
hostnames your tools can look up
58
categories to roll into risk tiers
Pipeline

The Enrichment Flow

How a raw domain becomes an enforced decision across your security stack

1
Observe

A tool in your stack sees a domain — in a log, a DNS query, a proxy request, or an email URL.

2
Enrich

The domain is looked up against the database, returning category, sub-type, and content-risk signals in under 10ms.

3
Score

Categories are mapped to your risk tiers, producing a single, consistent risk level for the destination.

4
Act

Policy or a SOAR playbook fires — block, allow, alert, or investigate — based on the category and risk.

This four-step loop is deliberately tool-agnostic. Whether the observation point is a next-generation firewall, a DNS resolver, a Splunk search, or an email gateway, the enrichment and scoring steps are identical, and only the final action differs.
That uniformity is what lets you write category-based policy once and apply it everywhere, and it is why teams that adopt a shared intelligence layer find their tooling easier to reason about over time.

The enrichment step can run inline for real-time enforcement or in batch for retrospective analysis.

Inline

Inline, the API answers fast enough to sit in the path of a DNS response or a proxy decision.

Batch

In batch, you can replay months of historical logs through the same classification to hunt for connections that were risky in hindsight, using the offline mirror so bulk enrichment never leaves your network.

Integration surface

Integration Patterns by Platform

Where content risk intelligence plugs into each layer of the stack

SIEM
SOAR
Gateway & Proxy
DNS & Firewall
1

SIEM Enrichment

Enrich firewall, proxy, and DNS logs with domain categories at ingest or search time.

Correlation rules can then reason about categories rather than opaque domains — for example, "alert when a finance-VLAN host connects to a file-sharing or paste-site domain outside business hours."
A single category field transforms raw telemetry into hunting-ready intelligence in Splunk, QRadar, Sentinel, or Elastic.
2

SOAR Playbook Automation

Drive category-aware playbooks. When a suspicious email or alert is triaged, the playbook queries the database for every URL involved, scores the categories, and executes a proportionate response:

  • block high-risk categories at the firewall
  • sweep endpoints that touched them
  • notify affected users
  • open a case — all without waiting on manual classification
3

Secure Web Gateway & Proxy

Augment a cloud or on-premises proxy with an independent categorization source. The database:

  • provides a second opinion on classification
  • catches newly registered domains the gateway vendor has not yet rated
  • fills coverage gaps for regional and niche domains, tightening policy at the exact point where user traffic is inspected
4

DNS & Firewall Feeds

Feed category data into DNS resolvers via RPZ and into next-generation firewalls via external dynamic lists or content-classification feeds.

Enforcement then happens at the network edge, blocking or shaping entire categories — phishing, malware, unsafe content, or high-bandwidth streaming — before traffic reaches internal systems.
See our DNS filtering integration guide for resolver-level detail.

RESTful API

Query categories and content-risk signals via a simple REST API with sub-10ms responses and batch lookups of up to 100 domains per request for high-throughput enrichment pipelines.

Offline Mirror

Mirror the full corpus locally for air-gapped or latency-critical environments, with hourly delta feeds so enrichment continues even during an internet disruption and bulk data never leaves the network.

Syslog & CEF Output

Emit categorization decisions in Syslog or Common Event Format for direct ingestion by any SIEM, over TCP, UDP, or TLS transport to Splunk, QRadar, Sentinel, or Elastic.

Inputs for a scoring rule

What an analyst's enrichment column could show for these hosts

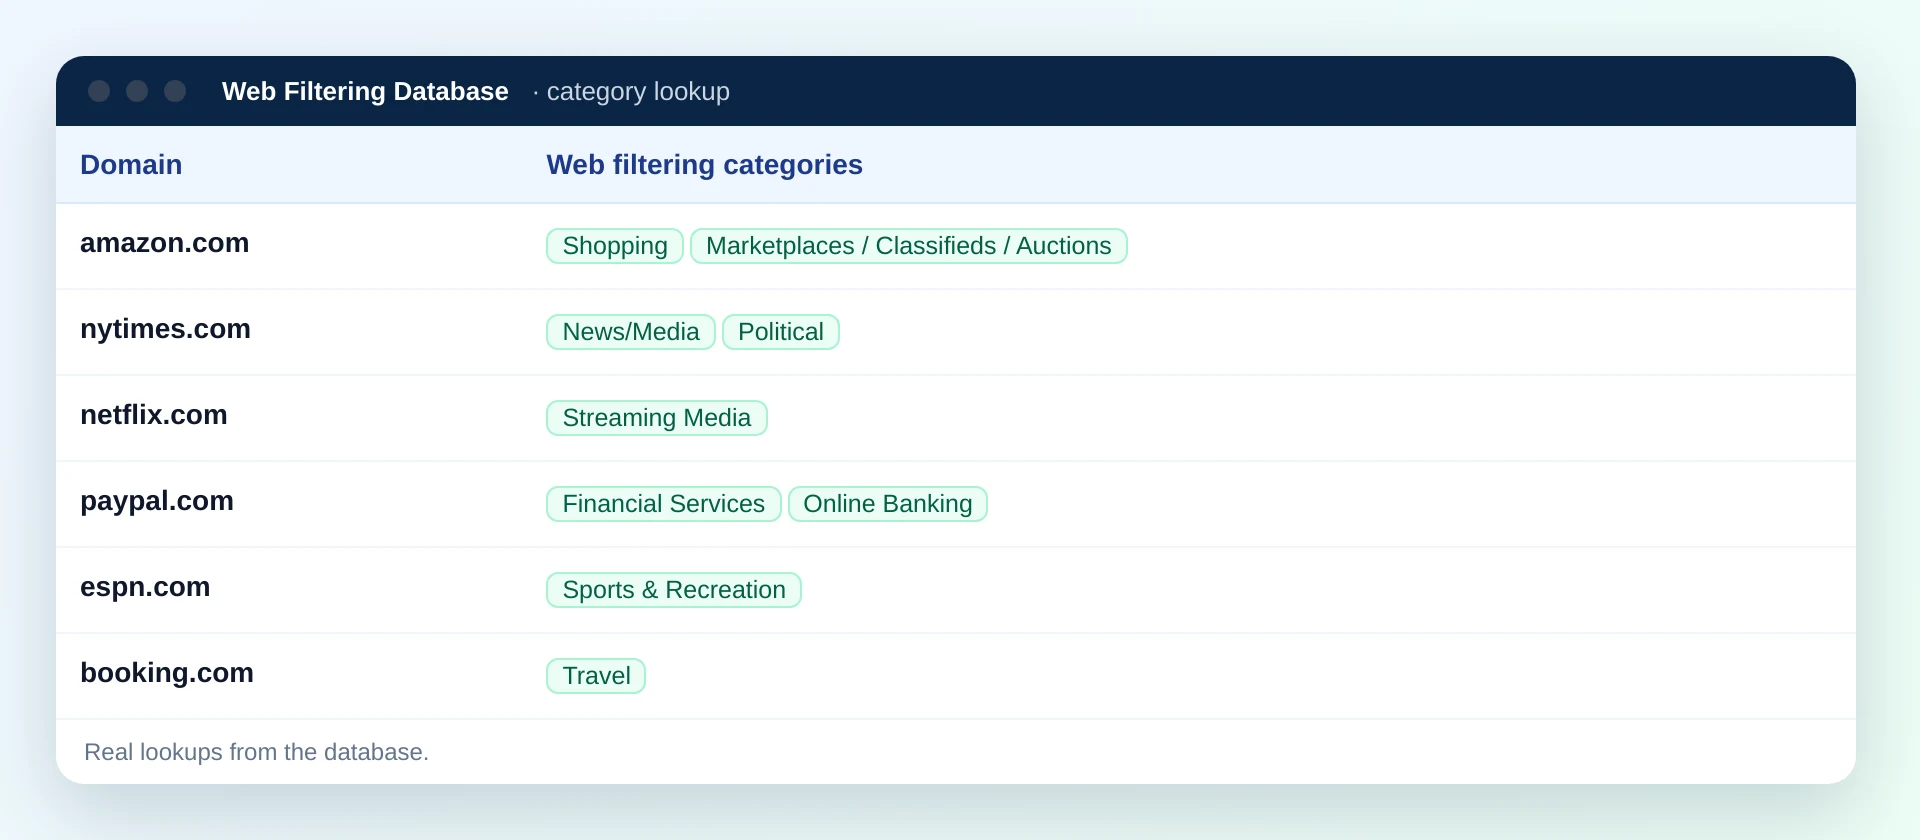
A category is a starting point for a risk tier, and you decide what each tier means in your environment. These rows are what the lookup returns today.

Hostname in the logCategories returned
tinyurl.comCDN / Hosting / Infrastructure, URL Shorteners
anydesk.comRemote Access Tools
telegram.orgEmail and Messaging, Social Networking
discord.comEmail and Messaging, Social Networking, Gaming
blogspot.comBlogs/Personal Sites, Web-based Applications

Category-Based Risk Scoring

Categories describe what a domain is; risk scoring decides how much you care.

The most durable integrations keep these two concerns separate: the database supplies an objective, consistent classification, and your organization maps those 58 categories to its own risk tiers based on its policy, industry, and threat model.

A financial-services firm may rate anonymizers and file-sharing as critical while treating streaming as merely a bandwidth concern; a school rates unsafe content and adult categories as critical while allowing educational tools freely.
Because the classification is the same for everyone and only the risk mapping differs, you get consistency where it matters and flexibility where it counts. The mapping lives in your policy engine, so you can tune it without touching the intelligence source.
Multi-label classification makes the scoring richer. A domain that is both file-sharing and unsafe content can be scored on its highest-risk facet, and secondary categories give analysts the context to understand why a destination was flagged. This is far more actionable than a single opaque score, because the reason travels with the number.
Objective categories, your risk tiers
  • Objective classification, subjective riskThe database classifies consistently; your organization owns the risk mapping and can tune it per policy.
  • Multi-label contextEvery applicable category is returned, so risk can be scored on the highest-risk facet with full context.
  • Tier-mapped enforcementMap categories to low, medium, high, and critical tiers that drive block, allow, alert, and investigate actions.
Inline or retrospective

Run enrichment next to the tool that needs it

The data lives inside your own systems, which keeps lookups in milliseconds and keeps your hostnames in house. Use the API where you want it hosted, and the files or offline database where you do not.

In production

Real-Time Enrichment Use Cases

Where content risk intelligence changes outcomes in production security operations

Alert Triage & Prioritization

Analysts drown in alerts that lack context. Enriching every domain with a category and risk tier lets the SOC auto-prioritize: a connection to a critical-risk phishing or malware category jumps the queue, while a streaming or shopping destination is deprioritized, so scarce analyst time goes where the risk actually is.

Email & URL Defense

Email gateways and phishing-response playbooks classify every embedded URL at delivery and click time. High-risk categories are blocked or rewritten, and the category context is attached to the case so responders see immediately whether a link led to phishing, file-sharing, or a benign business site.

Shadow IT & DLP

Category enrichment surfaces unsanctioned tools by class: file-sharing, consumer cloud storage, and anonymizers stand out against sanctioned business software. Feeding this into DLP and CASB policy closes exfiltration routes while keeping approved services open. Learn more in our enterprise web security guide.

Threat Hunting

Hunters replay historical logs through batch classification to find connections that were risky in hindsight — a host that reached a newly categorized malware domain last month, or a cluster of file-sharing activity before a data-loss event — using the offline mirror so bulk enrichment stays in the environment.

Network Policy & QoS

Beyond security, category signals drive traffic engineering. Identifying streaming, gaming, and CDN traffic lets operators shape bandwidth and protect business-critical flows, using the same intelligence layer that powers security enforcement.

Compliance Evidence

Category-level logging produces auditable evidence of what was blocked and why, supporting acceptable-use, safeguarding, and regulatory reporting. Every decision carries the category that drove it, so compliance reviews reproduce the reasoning rather than trusting an opaque verdict.

Build it

API Integration for Content Risk Intelligence

Enrich a domain and score its category risk in a few lines of code

Category Enrichment & Risk Scoring

Classify a domain, map its categories to your risk tiers, and return an enforcement decision your stack can act on.

import requests

API_URL = "https://webfilteringdatabase.com/api/moderate.php"
API_KEY = "YOUR_API_KEY"

# Map categories to your organization's risk tiers
RISK_TIERS = {
    "critical": {"Phishing", "Malware", "Botnets", "Unsafe Content"},
    "high":     {"File Sharing", "VPN & Proxy", "Adult Content"},
    "medium":   {"Streaming", "Gaming", "Advertising"},
}

def enrich_and_score(domain):
    r = requests.post(API_URL, json={"api_key": API_KEY, "query": domain}).json()
    categories = set(r.get("categories", []))
    for tier in ("critical", "high", "medium"):
        if categories & RISK_TIERS[tier]:
            return {"domain": domain, "risk": tier,
                    "categories": list(categories)}
    return {"domain": domain, "risk": "low", "categories": list(categories)}

# Enrich a batch of observed domains for the SIEM
for d in ["paste-site.example", "slack.com", "login-verify.example"]:
    print(enrich_and_score(d))
const API_URL = 'https://webfilteringdatabase.com/api/moderate.php';
const API_KEY = 'YOUR_API_KEY';

const RISK_TIERS = {
    critical: new Set(['Phishing', 'Malware', 'Botnets', 'Unsafe Content']),
    high:     new Set(['File Sharing', 'VPN & Proxy', 'Adult Content']),
    medium:   new Set(['Streaming', 'Gaming', 'Advertising'])
};

async function enrichAndScore(domain) {
    const res = await fetch(API_URL, {
        method: 'POST',
        headers: { 'Content-Type': 'application/json' },
        body: JSON.stringify({ api_key: API_KEY, query: domain })
    });
    const r = await res.json();
    const cats = new Set(r.categories || []);
    for (const tier of ['critical', 'high', 'medium']) {
        if ([...cats].some(c => RISK_TIERS[tier].has(c)))
            return { domain, risk: tier, categories: [...cats] };
    }
    return { domain, risk: 'low', categories: [...cats] };
}

['paste-site.example', 'slack.com'].forEach(async d =>
    console.log(await enrichAndScore(d)));
# Enrich a single domain with category and risk context
curl -X POST "https://webfilteringdatabase.com/api/moderate.php" \
  -H "Content-Type: application/json" \
  -d '{
    "api_key": "YOUR_API_KEY",
    "query": "paste-site.example"
  }'

# Example response:
# {
#   "domain": "paste-site.example",
#   "primary_category": "File Sharing",
#   "categories": ["File Sharing", "Unsafe Content"],
#   "risk_level": "high",
#   "risk_score": 78
# }
<?php
// Content risk intelligence enrichment
$apiUrl = 'https://webfilteringdatabase.com/api/moderate.php';
$apiKey = 'YOUR_API_KEY';

$riskTiers = [
    'critical' => ['Phishing', 'Malware', 'Botnets', 'Unsafe Content'],
    'high'     => ['File Sharing', 'VPN & Proxy', 'Adult Content'],
    'medium'   => ['Streaming', 'Gaming', 'Advertising'],
];

function enrichAndScore($domain, $apiUrl, $apiKey, $tiers) {
    $ch = curl_init($apiUrl);
    curl_setopt($ch, CURLOPT_POST, true);
    curl_setopt($ch, CURLOPT_POSTFIELDS, json_encode(['api_key' => $apiKey, 'query' => $domain]));
    curl_setopt($ch, CURLOPT_HTTPHEADER, ['Content-Type: application/json']);
    curl_setopt($ch, CURLOPT_RETURNTRANSFER, true);
    $r = json_decode(curl_exec($ch), true);
    curl_close($ch);
    $cats = $r['categories'] ?? [];
    foreach (['critical', 'high', 'medium'] as $tier) {
        if (array_intersect($cats, $tiers[$tier]))
            return ['domain' => $domain, 'risk' => $tier];
    }
    return ['domain' => $domain, 'risk' => 'low'];
}

print_r(enrichAndScore('paste-site.example', $apiUrl, $apiKey, $riskTiers));
?>
Field-tested

Integration Best Practices

1

Treat the classification as an intelligence source, not a policy

Keep the category-to-risk mapping in your own policy engine so you can tune enforcement — tightening a category to critical or relaxing it — without changing the intelligence feed. This separation is what keeps a large deployment maintainable as your threat model evolves.

2

Cache aggressively but not indefinitely

Domain classifications are stable enough to cache for enrichment throughput, yet the category can change when a domain is repurposed, so honor the hourly deltas to expire stale entries. For inline enforcement paths, a short local cache in front of the API keeps latency low while the deltas keep it accurate.

3

Log the category that drove every decision

When an alert fires or a request is blocked, recording the category and risk tier alongside it makes investigations faster and audits reproducible — the reasoning travels with the event instead of living only in a policy document.

4

Prove value on one integration, then expand

Finally, start with a single high-value integration, such as SIEM enrichment or DNS-level blocking of critical categories, prove the value, and expand from there rather than rewiring the whole stack at once.

Enrich from one licensed layer or from many separate lists

The gap shows when your team investigates an alert.

During an investigationList per toolOne category source
Same host in two toolsMay be labeled differently or not at allIdentical categories everywhere
Reach of the labelsLimited to each list's coverage120M+ categorized domains, 99.99% of the active internet
Hosts that serve several purposesOne tagSeveral categories where a site fits more than one
Newest hostnamesWait for the next list updateAbout 300,000 categorized daily
Changing a policyEdit every tool separatelyChange the category-to-tier map once
See which plan suits your stackLearn about OEM licensing

Database plans begin at $999 for the 1 million most popular domains. A security product that includes the data can take an OEM licence from $10,000 per year.

Integrate Content Risk Intelligence

Turn 120 million classified domains and 58 categories into real-time enrichment and category-based risk scoring across your SIEM, SOAR, gateway, DNS, and proxy stack.