webfilteringdatabase.com
Home Find Your Solution
Features
Domain Categorization API Real-Time Classification 58 Filtering Categories Offline Database (120M) SaaS App Hostnames Managed DNS Filter ML Classification Content Classification
Industries
K-12 Schools Corporate Healthcare Government ISPs
Tools
Domain Lookup Bulk Categorization Category Explorer
Resources
Pricing API Documentation Login / Sign Up
content classification

Content Classification Integration

How real-time classification feeds, behavioral analysis, and indicator correlation power our security categories to detect unsafe content, and C2 infrastructure

Query content risk Data

content classification as a Foundation

Web filtering is not just about content categorization -- it is a critical layer of cybersecurity defense. Our eight security-focused content categories (unsafe content, Spam, Botnets & C2, Cryptomining, Scam & Fraud, Newly Registered Domains, and Dynamic DNS) are powered by a dedicated content classification pipeline that operates independently from content classification.

Unlike content categories that can tolerate update latencies of hours or days, security categories must reflect the content risk landscape in near-real-time. A restricted content site can be stood up in minutes and may only remain active for a few hours. Our content classification pipeline ingests classification indicators (classifications) from over 40 external feeds and internal detection systems, correlates them, validates them, and pushes updates to the classification database within 90 seconds of initial detection.

This dual-pipeline architecture means that the categorization API always reflects the latest content risk data, even for domains that were safe an hour ago and have since been compromised or weaponized.
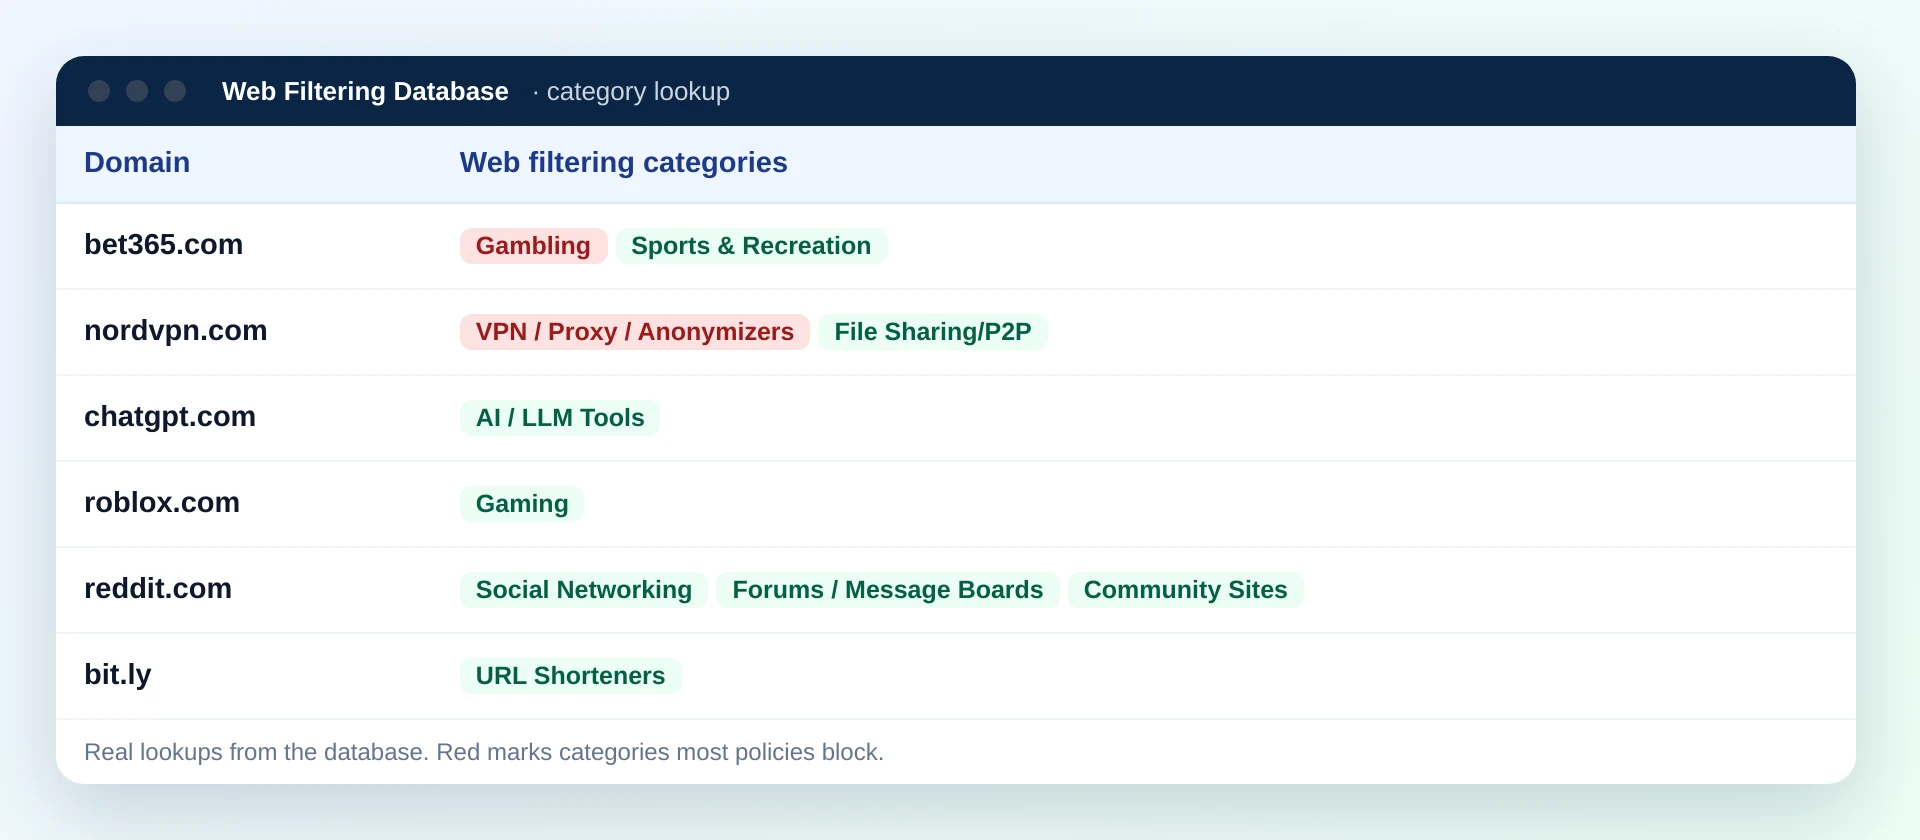
Add context to your feeds

A feed says a domain is bad, a category says what it is

Alert and indicator feeds are short and focused, so most of the traffic you see never appears in them. Category data adds a label to every other domain and helps your team decide what to look at first.

  • Join each indicator to the category of its domain before it reaches an analyst.
  • Treat anonymizers, shorteners and remote access tools differently from ordinary sites.
  • Use files, the real-time API or an offline database, whichever fits your tool.
Domain category records joined to security indicators
58
category labels to attach to an indicator
99.99%
of active sites that carry a label
120M+
domains behind the context you add

Detection Performance

content filtering metrics measured across production traffic and validated against industry benchmarks

99.6%
unsafe content Detection Rate
99.2%
restricted content Detection Rate
<90s
content risk Update Latency
40+
External classification feeds
unsafe content Detection

Identifies exploit kits, drive-by downloads, ransomware, and trojans

restricted content Detection

Visual similarity, URL pattern, and brand impersonation analysis

C2 & Botnet Detection

DNS traffic patterns, DGA detection, and beacon interval analysis

Intelligence Sources and Feed Integration

Multiple overlapping intelligence sources ensure comprehensive content risk coverage

1

Commercial classification feeds

We ingest indicators from leading commercial content classification providers that maintain global honeypot networks, unsafe content sandboxes, and restricted content monitoring infrastructure. These feeds deliver curated, validated classifications including malicious domains, IPs, URL patterns, and file hashes associated with active campaigns. Feed updates arrive via TAXII/STIX protocols every 60 seconds.

2

Open Source Intelligence (OSINT)

Community-maintained blocklists, academic research feeds, CERT advisories, and crowdsourced content risk databases provide broad baseline coverage. We aggregate over 20 OSINT feeds including abuse.ch URLhaus, PhishTank, OpenPhish, DShield, and SANS Internet Storm Center data. Cross-referencing multiple OSINT sources reduces false positives from any single feed.

3

Internal Detection Systems

Our own detection infrastructure includes DNS sinkholes, passive DNS sensors, web crawlers visiting newly registered domains, and automated unsafe content sandboxes that detonate suspicious downloads. These internal systems detect content risks that external feeds have not yet cataloged, giving our customers protection during the critical early hours of a new campaign.

4

Customer Telemetry

Anonymized, aggregated query patterns from customers who opt into content risk sharing reveal emergent content risks. A sudden spike in queries for previously dormant domains, or unusual query patterns from known-compromised network segments, triggers automated investigation. This crowd-sourced detection layer catches targeted attacks and zero-day campaigns that other feeds miss.

Labels analysts act on

Domains that often show up in investigations

File drops, paste sites and remote access tools appear in many incidents without any feed flagging them. Their category is what moves them up the queue.

DomainCategory in the data
pastebin.comDeveloper Tools / Code Hosting, Cloud Storage / File Hosting
mega.nzCloud Storage / File Hosting
anydesk.comRemote Access Tools
teamviewer.comFreeware/Software, Remote Access Tools
bit.lyURL Shorteners

Advanced Detection Techniques

Beyond simple indicator matching, our content classification pipeline employs behavioral and structural analysis to identify content risks that have never been seen before. Domain Generation Algorithm (DGA) detection uses character-level neural networks to identify randomly generated domain names used by botnets to contact their command servers, even before those domains are registered or contacted.

Fast-flux detection identifies domains that rapidly rotate their DNS A records across hundreds of IP addresses, a technique used to make botnet infrastructure resilient against takedowns. Our passive DNS database tracks resolution history and flags domains exhibiting this pattern within minutes of the first observation.

For restricted content detection, we deploy visual similarity analysis that renders suspected restricted content pages and compares them against a library of known brand login pages using perceptual hashing and structural similarity metrics. This catches restricted content pages even when the URL and content text differ from known templates, because the visual appearance is designed to fool human victims.

DGA Detection

Character-level LSTM networks identify algorithmically generated domain names with 98.7% accuracy, detecting botnet rendezvous domains before they are activated.

Fast-Flux Identification

Passive DNS monitoring flags domains cycling through IP addresses at abnormal rates, revealing bulletproof hosting and botnet fast-flux networks.

Visual restricted content Analysis

Perceptual hashing compares rendered page screenshots against 5,000+ brand templates to detect impersonation attacks regardless of URL or text content.

Infrastructure Correlation

Shared hosting IPs, SSL certificate fingerprints, and WHOIS registrant data link unknown domains to known content risk actor infrastructure clusters.

Domain Age Scoring

Statistical models trained on millions of malicious and benign domains show that domains under 30 days old are 10x more likely to host content risks than established domains.

Behavioral Beaconing

Network traffic interval analysis detects the periodic check-in patterns of unsafe content communicating with C2 servers, even when encrypted or tunneled over DNS.

New domains, same day

The labels keep arriving while you investigate

About 300,000 new domains are categorized every day, so recently registered names are less likely to come up unlabeled. You can load the daily additions or ask the real-time API when something unfamiliar appears.

Real-Time Update Pipeline

The lifecycle of a content risk indicator from initial detection to customer protection follows a tightly optimized pipeline. When a new indicator is ingested -- whether from an external feed, internal detection, or customer telemetry -- it enters a validation queue. Automated checks verify that the indicator is not a false positive by cross-referencing against allowlists of known-good infrastructure, checking for CDN or cloud hosting IPs that could affect legitimate services, and validating domain syntax and reachability.

Validated indicators are assigned content risk types, severity scores, and confidence ratings, then published to the classification database. Edge nodes receive updates via persistent WebSocket connections, ensuring that the new content risk data is queryable worldwide within 90 seconds of validation. The real-time classification pipeline also incorporates these indicators, so even domains that have not been directly reported benefit from infrastructure-level correlation.

Indicators have configurable expiration policies. restricted content domains are typically delisted after 30 days of confirmed inactivity, while unsafe content and C2 domains remain flagged for 90 days. Expired indicators move to a historical archive accessible through the API's history endpoint, allowing security teams to investigate past exposures.

Indicator feeds alone compared with feeds plus categories

Adding a category column changes how much of your traffic you can describe.

AspectIndicator feed onlyFeed plus category database
Traffic describedOnly domains someone has flagged120M+ categorized domains
Unflagged destinationsNo informationA label such as Remote Access Tools or URL Shorteners
Prioritising alertsSame weight for every hitWeight by one of 58 categories
Newly seen domainsAbsent until reportedAbout 300,000 new domains labelled daily
DeploymentDepends on the feed providerFiles, API or offline database inside your systems
Check what the database containsRead about product licences

Database plans start at $999 and include the 1 million most popular domains. Security products that redistribute the data need an OEM licence, which begins at $10,000 per year.

Protect Your Network with Real-Time content classification

Integrate our content risk-enriched domain categorization into your security infrastructure. Block unsafe content, and C2 traffic before it reaches your users.

Access content classification API