webfilteringdatabase.com
Home Find Your Solution
Features
Domain Categorization API Real-Time Classification 58 Filtering Categories Offline Database (120M) SaaS App Hostnames Managed DNS Filter ML Classification Content Classification
Industries
K-12 Schools Corporate Healthcare Government ISPs
Tools
Domain Lookup Bulk Categorization Category Explorer
Resources
Pricing API Documentation Login / Sign Up
Content Category

CDN & Infrastructure Filtering

Classify content-delivery networks, edge caches, and hosting infrastructure with precision. Over 900,000 CDN and infrastructure domains identified through multi-signal detection for accurate allow-listing and traffic management across our 120 million domain database.

How CDN Domains Are Identified

The CDN and infrastructure category covers content-delivery networks, edge-cache endpoints, object-storage and asset-hosting domains, and the shared platform infrastructure that serves resources for thousands of unrelated websites. Unlike most categories, the value here is usually about knowing what NOT to block: CDN domains underpin legitimate services across every other category, and mis-blocking them breaks large swaths of the web at once.

Identification combines analysis of asset-serving patterns, cache and edge headers, and object-storage URL structures with ASN and IP-range mapping of the major CDN and cloud providers. Because a single CDN endpoint may serve images for a news site, scripts for a bank, and video for a streaming service, correct classification prevents an over-broad block from taking down unrelated legitimate traffic.

CDN classification is deliberately kept distinct from the content it delivers. The API surfaces the infrastructure signal separately so a policy can act on the underlying website category while treating shared delivery infrastructure with the caution it requires.
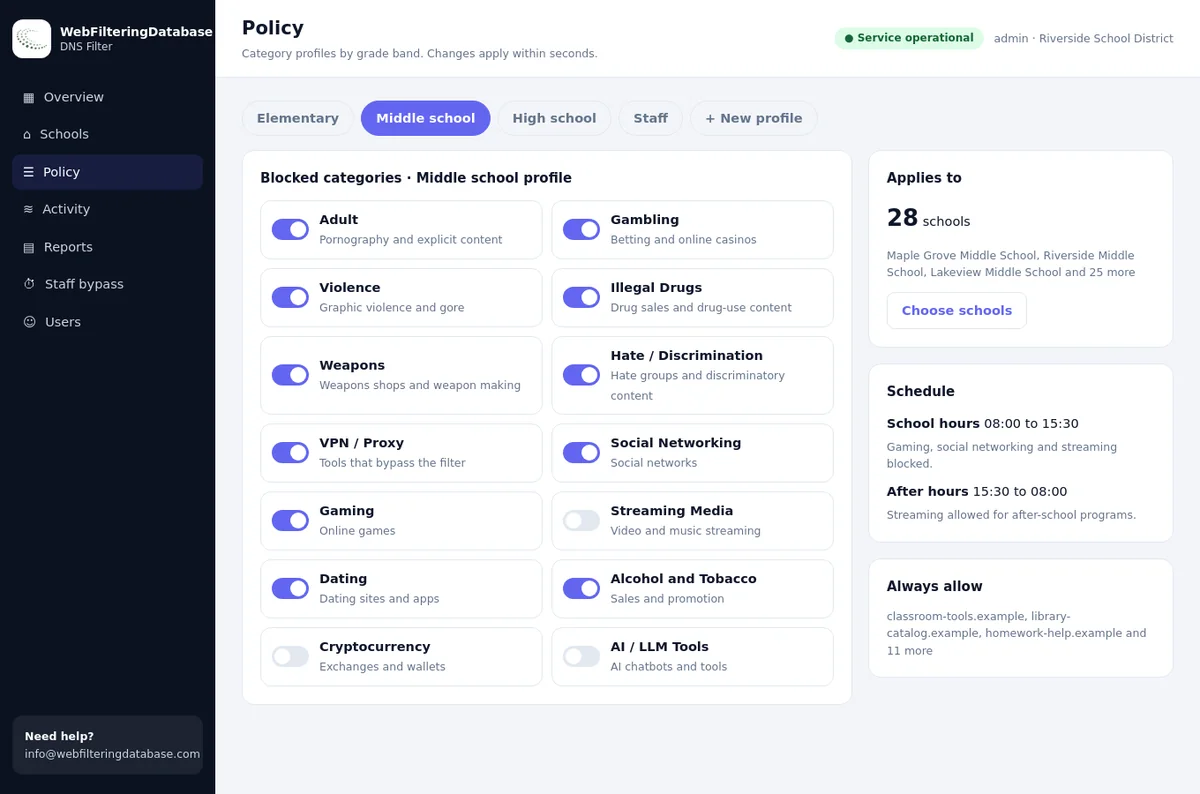
Allow the plumbing, block the rest

Keep CDN hosts open while the categories you block stay blocked

A CDN label covers hosts that deliver pages for thousands of other sites, so a filter must tell delivery from content. Our managed DNS filter uses the same database behind this category, so you switch categories per site and leave delivery traffic alone.

  • Block Gaming or Streaming Media by category without breaking the shared hosts those pages load from.
  • An always-allow list covers the odd host your own app depends on, and changes apply in seconds.
  • Everything is set from one dashboard, with no appliance or agent to install.
Category switches in the managed DNS filter where CDN stays allowed
120M+
domains carrying a label, delivery networks included
22
blocking categories you can switch per site
Milliseconds
response time for each DNS lookup

Understanding the CDN Category

Shared infrastructure that should almost always be allowed

CDN and infrastructure is the one category where the default correct action is usually allow, not block. Content-delivery networks exist precisely because they serve assets for enormous numbers of unrelated sites from shared endpoints. Blocking a CDN domain to stop one undesirable site will simultaneously break the images, scripts, fonts, and video that thousands of legitimate sites depend on, producing a cascade of hard-to-diagnose failures that look like an outage rather than a policy.

The right use of CDN classification is therefore to inform other decisions rather than to drive blocking directly. Knowing that a domain is shared delivery infrastructure tells a policy engine to make its allow/deny decision based on the underlying content category instead of the CDN domain, and tells a network operator that this endpoint is load-bearing infrastructure to be shaped carefully, not blocked. In the rare cases where a CDN endpoint is dedicated to undesirable content, the classification still surfaces that so a targeted decision is possible.

Content-Delivery Networks

Global CDN and edge-cache providers that serve static and streamed assets for large numbers of unrelated origin sites.

Object & Asset Storage

Cloud object-storage and asset-hosting endpoints that back downloads, images, and application resources across many customers.

Cloud Platform Infrastructure

Shared cloud-platform hostnames and PaaS endpoints used by numerous applications, requiring content-based rather than domain-based policy.

Edge & Acceleration

Edge-compute, acceleration, and reverse-proxy front-ends that sit in front of many origins and must not be blocked as a unit.

Delivery networks in the data

How CDN and hosting names are labelled

Delivery networks carry their own label, separate from the sites they serve. These entries come straight from our database.

HostLabels in our database
cloudflare.comCDN / Hosting / Infrastructure, Computers & Technology
fastly.comCDN / Hosting / Infrastructure
cdnjs.comCDN / Hosting / Infrastructure
godaddy.comCDN / Hosting / Infrastructure, Parked / For-Sale Domains
namecheap.comCDN / Hosting / Infrastructure, Parked / For-Sale Domains

Detection Methodology

Multiple classification signals combine for accurate CDN identification

Cache & Edge Header Analysis

CDN endpoints expose characteristic cache-status, edge-location, and acceleration headers. Analyzing these response signals identifies delivery infrastructure distinct from origin websites.

ASN & IP-Range Mapping

Major CDN and cloud providers announce known ASNs and IP ranges. Mapping domains to this infrastructure classifies delivery endpoints reliably even when hostnames are opaque or auto-generated.

Asset-Serving Patterns

Object-storage URL structures, versioned asset paths, and static-resource-only responses mark asset-hosting endpoints. Recognizing these patterns separates pure delivery from interactive origins.

Multi-Tenancy Detection

Shared endpoints that serve resources for many unrelated origins exhibit detectable multi-tenancy. Identifying this prevents an over-broad block against infrastructure used by thousands of legitimate sites.

Traffic-Profile Signals

Delivery infrastructure shows a distinctive high-volume, cache-heavy traffic profile. These signals help operators treat CDN endpoints as load-bearing infrastructure for shaping rather than blocking.

Continuous Re-classification

Providers add edge regions and endpoints continuously. Continuous ASN and endpoint mapping keeps the infrastructure classification accurate as delivery networks expand.

Policy & Use Cases

CDN classification supports safe allow-listing and traffic management

Accurate Allow-Listing

Knowing which domains are shared delivery infrastructure lets policy engines avoid the classic mistake of blocking a CDN to stop one site. Allow-listing infrastructure and deciding on content elsewhere keeps the web working while policy is enforced.

  • Prevents cascading breakage from CDN blocks
  • Directs allow/deny to the content category
  • Reduces false-positive support tickets
  • Keeps legitimate assets and scripts loading
  • Applies across managed and BYOD devices

Traffic Management

Network operators treat CDN endpoints as load-bearing infrastructure to be shaped, not blocked. Classification identifies these high-volume endpoints so they can be prioritized or scheduled without disrupting the sites that depend on them.

  • Identifies high-volume delivery endpoints
  • Enables careful shaping over hard blocks
  • Feeds QoS and capacity-planning decisions
  • Distinguishes delivery from origin traffic
  • Supports off-peak scheduling of large assets

Security Context

When investigating suspicious traffic, knowing that a destination is shared CDN infrastructure changes the analysis. It prevents mis-attribution and directs security teams to the underlying content rather than the delivery layer.

  • Prevents mis-attribution of shared endpoints
  • Adds infrastructure context to SIEM data
  • Flags rare CDN endpoints dedicated to abuse
  • Supports accurate incident triage
  • Integrates with firewall and proxy logs

Application Reliability

Developers building filtering products use CDN classification to avoid breaking their own users. Treating infrastructure correctly keeps applications, fonts, and scripts loading even under strict content policy.

  • Avoids breaking application dependencies
  • Keeps fonts, scripts, and images loading
  • Content-based policy over domain-based blocks
  • Sub-10ms lookups for inline decisions
  • Batch endpoints for pre-load allow-lists

CDN Category Statistics

Coverage and accuracy metrics for the CDN and infrastructure category

900K+
CDN Domains Identified
99.6%
Classification Accuracy
<0.1%
False Positive Rate
Hourly
Classification Updates

Why CDNs Should Rarely Be Blocked

The single most common self-inflicted outage in web filtering is blocking a CDN. Because content-delivery networks serve assets for thousands of unrelated sites from shared endpoints, a block aimed at one undesirable site takes down the images, scripts, fonts, and video of countless legitimate ones. The symptoms — half-loaded pages, missing styling, broken applications — look like an infrastructure failure, and the root cause is often hard to trace back to the filtering rule that caused it.

The correct pattern is to classify CDN infrastructure explicitly and then make allow/deny decisions on the underlying content category rather than the delivery domain. Our classification exists largely to enable this: it tells your policy engine "this is shared infrastructure, do not block it as a unit," and directs the real decision to the content being delivered. In the rare case where a CDN endpoint is dedicated to a single undesirable use, the classification surfaces that too, so a precise block remains possible.

Because the infrastructure signal is exposed separately from content, the enforcement decision stays clean. The classification tells you when you are looking at load-bearing delivery infrastructure; your policy applies content rules where they belong and leaves the plumbing intact.

Shared hosting, one rule

Exceptions without rewriting the policy

Category switches work per site, and always-allow and always-block lists sit on top of them. One awkward shared host can be handled by hand while everything else follows the category.

Integration Guide

Use CDN classification to protect allow-lists across DNS, proxy, and security layers

Deployment Options

In DNS and proxy deployments, CDN classification is used defensively: before a block rule fires, the policy checks whether the domain is shared delivery infrastructure and, if so, defers the decision to the underlying content category. This prevents the cascading breakage that blanket CDN blocks cause.

In firewall and QoS deployments, CDN classification identifies the high-volume, load-bearing endpoints that should be shaped carefully rather than blocked. Operators use it to prioritize or schedule delivery traffic while keeping dependent sites functional.

For developers building filtering products, the real-time API returns infrastructure and content signals separately with sub-10ms latency, so applications can enforce content policy without breaking their own asset loading. Batch endpoints support pre-loading infrastructure allow-lists.

  • DNS RPZ feeds updated every 15 minutes
  • ICAP/ECAP support for web proxy integration
  • REST API with sub-10ms response times
  • SDKs for Python, Node.js, Go, Java, and C#

Domain Classification API

// Check cdn classification
curl -X POST "https://webfilteringdatabase.com/api/moderate.php" \
  -H "Content-Type: application/json" \
  -d '{"api_key": "YOUR_API_KEY", "query": "assets.example-cdn.net"}'

// Response
{
  "domain": "assets.example-cdn.net",
  "categories": ["CDN / Infrastructure"],
  "confidence": 0.99,
  "action": "allow"
}

DNS RPZ Config

# BIND RPZ configuration
zone "rpz.webfilteringdb.com" {
    type slave;
    masters { 198.51.100.1; };
    file "rpz-cdn.db";
};

options {
    response-policy {
        zone "rpz.webfilteringdb.com"
            policy nxdomain;
    };
};

Data Coverage & Taxonomy

The CDN / Infrastructure category is one of 58 content categories in the Web Filtering Database taxonomy, applied consistently across a corpus of more than 120 million classified domains. Every domain is evaluated with a multi-label model, so a site can carry the CDN classification alongside any related categories it also belongs to. This multi-label design is what lets policy engines reason about overlap instead of forcing each domain into a single bucket.

Classifications are delivered three ways to fit different architectures. The real-time REST API returns a result in under ten milliseconds and is ideal for inline DNS, proxy, and application enforcement. The offline database mirror provides the full corpus for on-premises deployments where lookups must never leave the network, refreshed by hourly delta feeds. And DNS RPZ feeds let firewalls and resolvers load category zones directly. Whichever delivery mode you choose, the CDN classification carries the same signals and sub-type detail described on this page.

Because the taxonomy is shared across every category, the CDN classification composes cleanly with the rest of your policy. You can express a single acceptable-use ruleset that spans dozens of categories, knowing each domain has been evaluated by the same pipeline and scored against the same 100-million-domain reference set.

Deployment Best Practices

Start by deciding whether the CDN category is a block, allow, or shape decision in your environment, because that choice drives everything downstream. Many categories are not simply "block everything" — the sub-type and secondary-category signals in every response exist precisely so you can write proportionate rules rather than blunt ones. Map the categories to your written acceptable-use or safety policy first, then translate that map into technical rules.

Prefer DNS-level enforcement for breadth: it covers every device and application that resolves a domain, including native apps and consoles, with no client software to deploy. Layer proxy or firewall inspection on top only where you need per-request granularity or content-aware decisions under SSL inspection. For latency-sensitive or air-gapped environments, use the offline mirror so enforcement continues even during an internet disruption.

Finally, treat classification as a living feed rather than a one-time import. The CDN category is re-scanned continuously as new domains appear and existing ones change, so consuming the hourly deltas keeps your policy accurate. Log category decisions to your SIEM for auditing and capacity planning, and review the edge cases the sub-type signals surface rather than reacting to individual domains one at a time.

Handling CDN traffic: by hand or with a managed filter

Delivery hosts change often, which is why hand-kept lists drift.

TaskDoing it by handManaged DNS filter
Telling delivery from contentRead logs and guess from hostnamesLabels from a database of 120M+ domains
Blocking a category cleanlyHunt down every host each page pulls inSwitch the category, allow the exceptions
New hosts appearingEdit the lists each timeCategory data keeps up, lists only for exceptions
Rolling out a changeTouch each router or deviceApplies in seconds
Several locationsRepeat the work per routerOne dashboard, many sites
Read about the managed filter for CDN hostsTalk to us about a pilot

CDN Filtering FAQ

Common questions about the CDN category

Should I block CDN domains to stop unwanted content?

Almost never. CDN endpoints serve assets for thousands of unrelated legitimate sites, so blocking one to stop a single undesirable site breaks images, scripts, and video across the web. The correct approach is to classify the CDN as infrastructure and make the allow/deny decision on the underlying content category instead.

Why does a filtering product need a CDN category at all?

To avoid breaking itself. A filtering engine that treats shared delivery infrastructure like any other domain will eventually block a CDN and take down large swaths of legitimate traffic. Classifying CDNs explicitly lets the policy engine recognize load-bearing infrastructure and route decisions to content, preventing cascading failures.

Can I still block a CDN endpoint that only serves bad content?

Yes. In the rare case where a specific CDN or object-storage endpoint is dedicated to a single undesirable use, the classification surfaces that so a targeted block is possible. The category is about caution with shared infrastructure, not a blanket exemption for every endpoint.

How does CDN classification help with bandwidth?

CDN endpoints are the high-volume, load-bearing part of most traffic profiles. Identifying them lets network operators shape or schedule delivery traffic carefully, prioritizing business-critical flows, rather than blocking infrastructure that thousands of dependent sites rely on.

How are CDN endpoints identified so accurately?

We combine cache and edge header analysis, ASN and IP-range mapping of the major providers, asset-serving URL patterns, and multi-tenancy detection. This layered approach achieves a 99.6% accuracy rate and a false-positive rate below 0.1%, which matters because errors here break legitimate sites at scale.

How do I access the CDN / Infrastructure classification via API?

Send a POST request to the classification endpoint with your API key and the domain to check, and the response returns the primary category, any secondary categories, sub-type detail, and a confidence score in under ten milliseconds. The same CDN data is also available as an offline database mirror with hourly deltas and as DNS RPZ feeds for firewalls and resolvers.

How accurate and current is the CDN category?

The category is maintained against a corpus of more than 120 million domains and re-scanned continuously, so new and changed domains are typically reflected within hours. Accuracy is validated on an ongoing basis, and the multi-label model means a domain carries every category that applies rather than being forced into one, which reduces both false positives and missed classifications.

Pricing follows the number of sites and devices you run. A pilot on a single site shows the blocks and reports before you commit.

Related Categories

Combine CDN filtering with related categories for comprehensive policy

Use CDN Classification for Safer Filtering

Protect your allow-lists and avoid cascading breakage with accurate identification of 900,000 CDN and infrastructure domains across the delivery ecosystem.